welcome to

tap to skip000%

0x5h4q: Daniel Bolaji-Busola, Penetration tester and security researcher

Daniel Bolaji-Busola · Lagos, NG

penetration tester & security researcher

I test web, Active Directory, and cloud environments, turn attack paths into clear evidence, and help teams fix the risks that matter.

Contact: princeheritage1@gmail.com

01 $ whoami

I'm a penetration tester and security researcher in Lagos. I find the interesting parts of systems: the trust that shouldn't be there, the path nobody drew on the diagram.

Most days I'm testing web applications, working through Active Directory attack paths, or soldering a board that probably shouldn't fit in a pocket. I study Computer Science at Covenant University, and I write up everything I learn so the next person gets there faster.

$ cat stats.json live
Hack The Box level
57
HTB rank in Nigeria
#2
Write-ups published
24+
TryHackMe
Top 6%

$ cat ~/.stack

languages tools platforms

  • Pythonlang
  • Burp Suitetool
  • Active Directoryenv
  • Bashlang
  • Nmaptool
  • Linuxenv
  • PowerShelllang
  • Impackettool
  • Kali Linuxenv
  • C++lang
  • BloodHoundtool
  • Windowsenv
  • TypeScriptlang
  • NetExectool
  • AWSenv
  • SQLlang
  • Wiresharktool
  • Firebaseenv
  • CircuitPythonlang
  • Metasploittool
  • Hack The Boxenv
  • Ghidratool
  • TryHackMeenv
  • Modbus / ICSenv
  • ESP32env
  • Arduinoenv
  • KiCadenv
  • Raspberry Pi Picoenv

02 $ ls experience/

Jun 2026 – Present · Remote

Cyber Core Associate

Ubuntu Bridge Initiative — Sankofa SOC

  • Completed 4-stage breach investigation for Sankofa Digital fintech: reconstructed full kill chain from SQLi/SSRF initial access through persistence (sudoers abuse, shell profile backdoor) to C2 beaconing and data exfiltration.
  • Identified insider threat where Head of Security engineered the breach by reopening dead tickets and manipulating board-level visibility of security controls.
  • Delivered board-ready remediation package: risk register, regulatory breach notification, 30/60/90-day roadmap, and control mapping with confirmed vs. exposed data separation.

Jul 2025 – Present · Remote

Security Researcher

HackerOne / BugCrowd / YesWeHack

  • Hunting web application vulnerabilities specialising in authentication flaws, IDOR, and API security.
  • Acknowledged in program hall of fame for disclosed findings.

Apr 2024 – Present · Ota, Nigeria

Security Engineer Apprentice

Covenant University

  • Performed authorized penetration tests simulating real-world cyber threats against university infrastructure.
  • Developed Python automation scripts for security audit workflows aligned with NIST and ISO 27001 compliance.

03 $ ls projects/

Labs, hardware and tools. Each one started with a question I wanted to answer properly.

sh4q logo
Latest release · v1.2.001

sh4q

Python, SQLite, DNS, HTTP

A safety-first reconnaissance control plane with scope-enforced DNS and HTTP resolution, redirect and DNS-rebinding validation, request budgets, and an event-sourced evidence store with tool-version provenance.

Outcome

Bounded recon with an auditable trail

View on GitHub

SafeCO screenshotICSC 2026 submission02

SafeCO

Python, SQLite, Modbus, ICS/OT

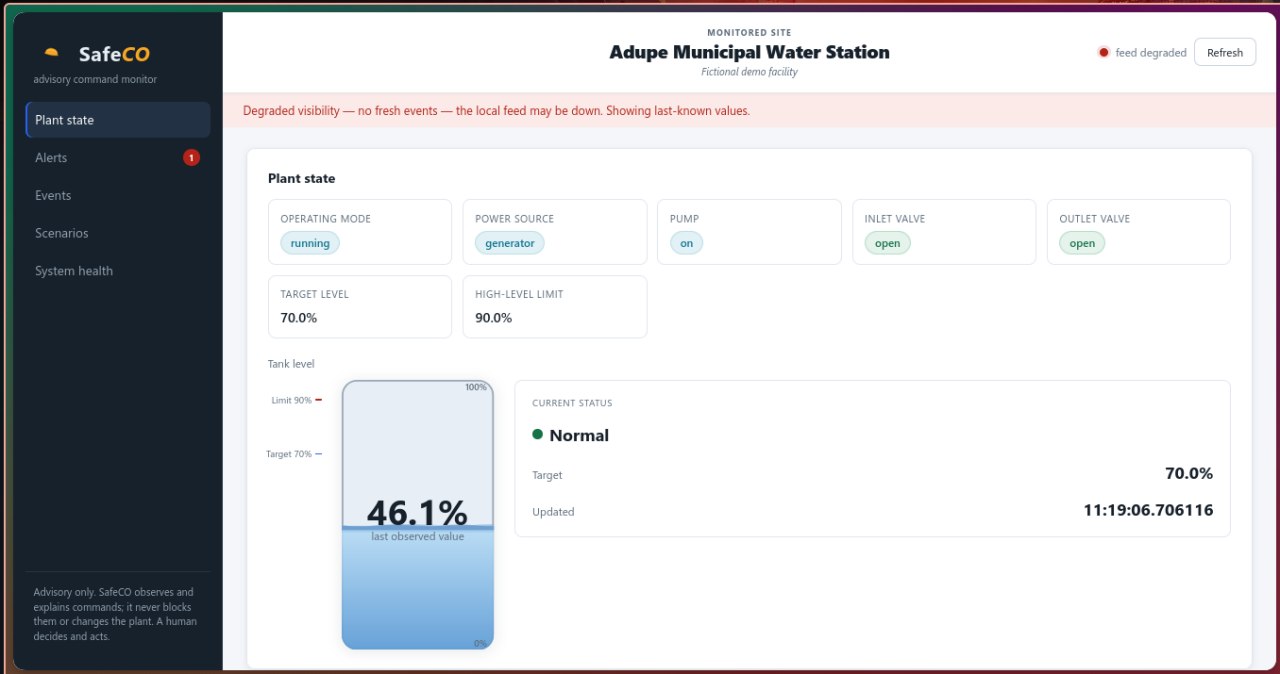
A local-first, explainable monitor for a simulated water-treatment plant. It flags protocol-valid but unsafe commands and advises a human operator through a tamper-evident, hash-chained event store.

Outcome

Human-readable safety signals for OT operators

View on GitHub

GDG Cyber Quiz screenshotCommunity03

GDG Cyber Quiz

Web app · Quizzes · CTF challenges · Leaderboard

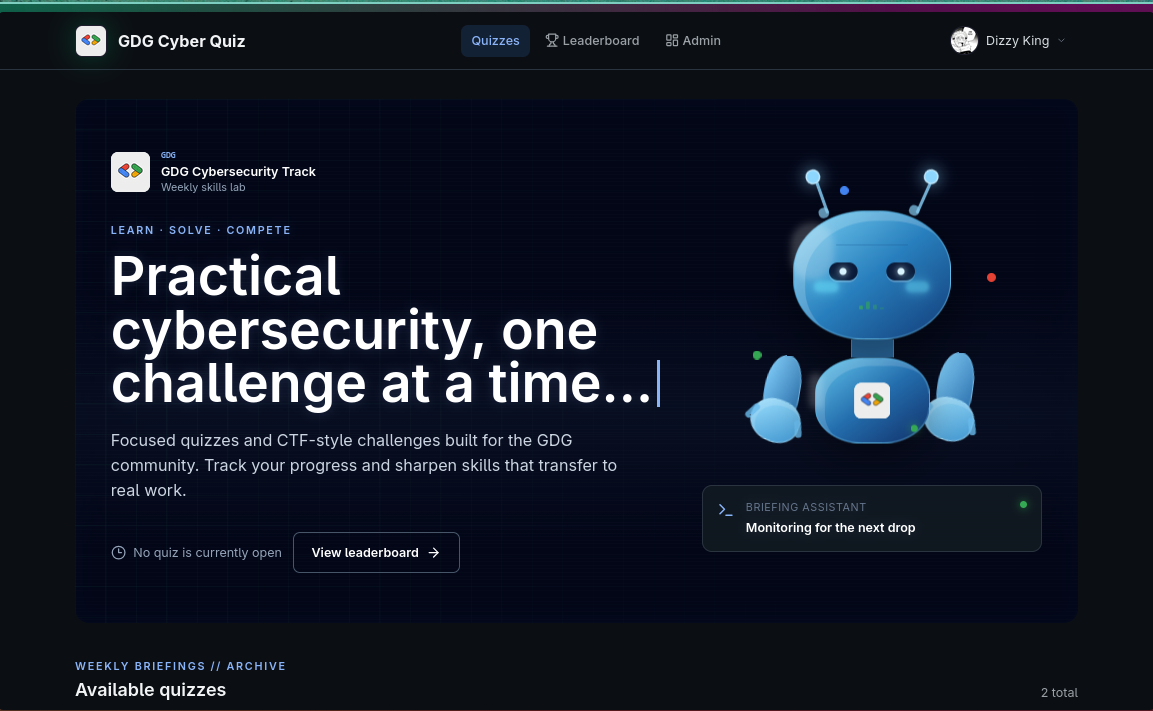
A weekly skills lab I built for the GDG cybersecurity track at my school: focused quizzes and CTF-style challenges, a live leaderboard, and an admin console for dropping new briefings.

Outcome

Weekly practice and friendly competition for GDG members

Open the live app

HTB Pro Labs & Fortresses screenshotOffensive security labs04

HTB Pro Labs & Fortresses

Active Directory, Cloud, Web

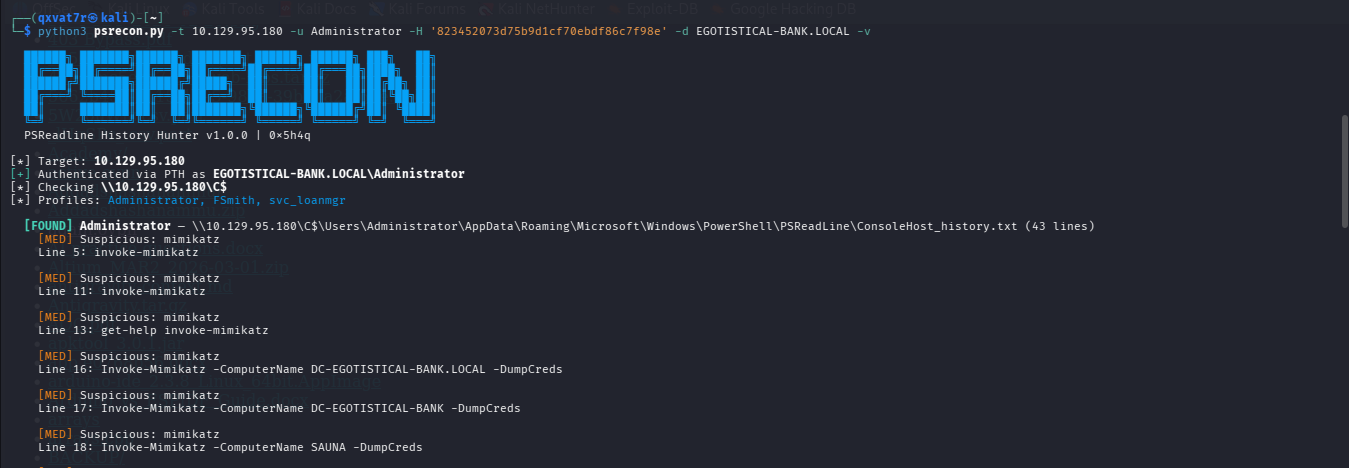
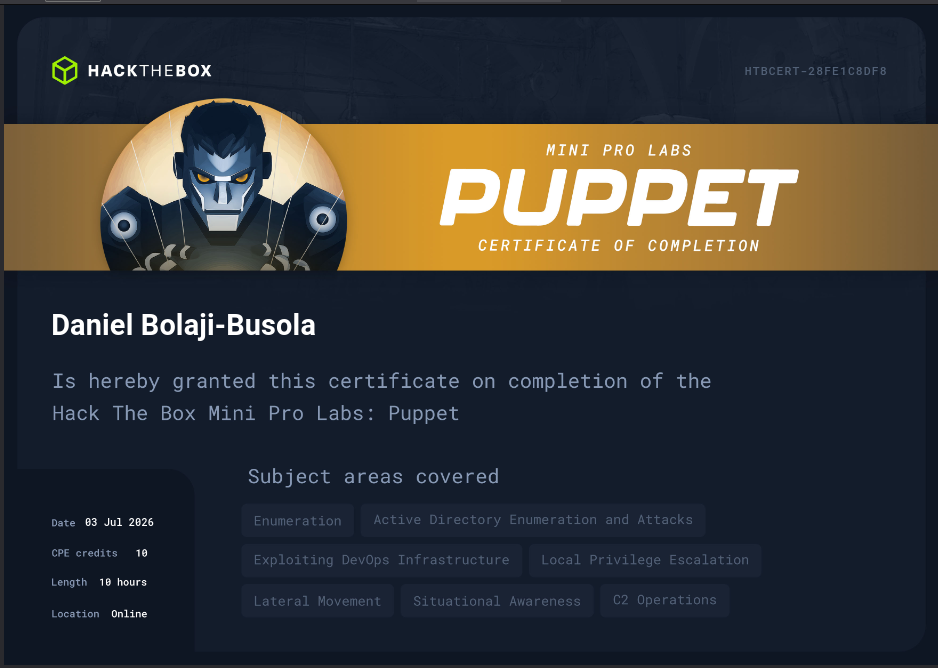
Completed Pro Lab Puppet and Fortresses Context and Akerva. Pwned Hard-rated machines (Pirate, Logging, TombWatcher) chaining advanced AD attacks: Pre2k, gMSA abuse, RBCD, SPN jacking, ADCS.

Outcome

Advanced AD attack-path practice

Read related research

ESP32 Marauder screenshotHardware security05

ESP32 Marauder

KiCad, C++, Arduino, ESP32

Custom carrier PCB integrating ESP32, TFT display, CC1101 sub-GHz RF module, GPS, and MicroSD. Supports deauth detection, BLE scanning, evil portal deployment, and PCAP capture.

Outcome

Portable wireless assessment platform
BadUSB / Rubber Ducky screenshotRed team hardware06

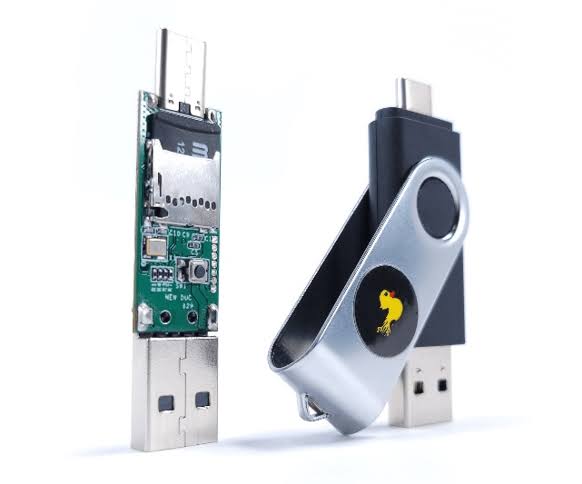
BadUSB / Rubber Ducky

Raspberry Pi Pico, CircuitPython

USB HID attack device for red team engagements: credential harvesting, reverse shell deployment, data exfiltration.

Outcome

Repeatable HID payload delivery

04 $ cat certs.txt

cert_01 Certified

PJPT

Practical Junior Penetration Tester

TCM Security

cert_02 Certified

CRTA

Certified Red Team Analyst

CyberWarfare Labs

cert_03 Top 2%

CTF

Cyber Apocalypse CTF 2026: The Salt Crown

Hack The Box

103rd of 6,744 teams · 136/136 challenges solved

cert_04 Holo tier

S11

Hack The Box Season 11

Hack The Box

Rank 776 of 12,396 · 11/13 root · 13/13 user flags

cert_05 Certified

ETH

Cyber Core Ethical Hacking Associate

Ubuntu Bridge Initiative

Open PDF

06 $ ls ~/tools

Small versions of things I use every week. They run entirely in your browser, so nothing you drop in here is uploaded anywhere.

$ chef --recipe runs locally

Operations

Recipe

  1. 1. To Base64

Input

Output

07 $ ping 0x5h4q

A security problem, a collaboration, an opportunity, or just a good CTF story. Email reaches me fastest. (^_^)/